Self-service portal
SecureSBOM
Sign and verify SBOMs with managed keys, API access, audit-ready workflows, and CI/CD integrations.
SecureSBOM portal
Sign and verify SBOMs with managed key infrastructure, CI/CD integrations, offline verification, and audit-ready evidence for modern software supply chain programs.
Support the trust expectations emerging in the 2026 SBOM minimum elements.
Avoid spreading private signing keys across build systems and developer machines.
Verify signed SBOMs in customer, regulated, and air-gapped workflows.
Self-service portal
Sign and verify SBOMs with managed keys, API access, audit-ready workflows, and CI/CD integrations.
AI supply chain metadata
A JSON Schema and reference project for describing AI models, datasets, infrastructure, relationships, and security properties.
Enterprise-grade cryptographic signing and validation for every SBOM you produce or consume.
Native support for CycloneDX signatures and detached SPDX verification, ensuring interoperability across ecosystems.
Describe AI models, datasets, infrastructure, relationships, and security metadata with a practical JSON Schema.
API-first design enables easy drop-in integration with existing DevSecOps pipelines (GitHub, GitLab, Jenkins, Bitbucket).
Support for Hardware Security Modules to protect signing keys in any environment.
Perform signing and verification in air-gapped or highly regulated environments with full offline support.
Modern software supply chain security is built on evidence. Organizations need confidence in what software contains, whe...
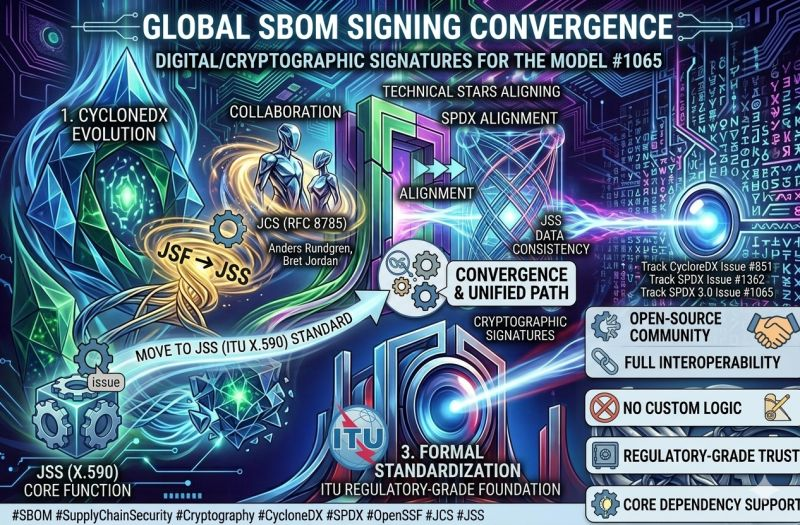
“Don’t roll your own crypto.” It’s the first rule of security engineering, and it turns out it’s ...
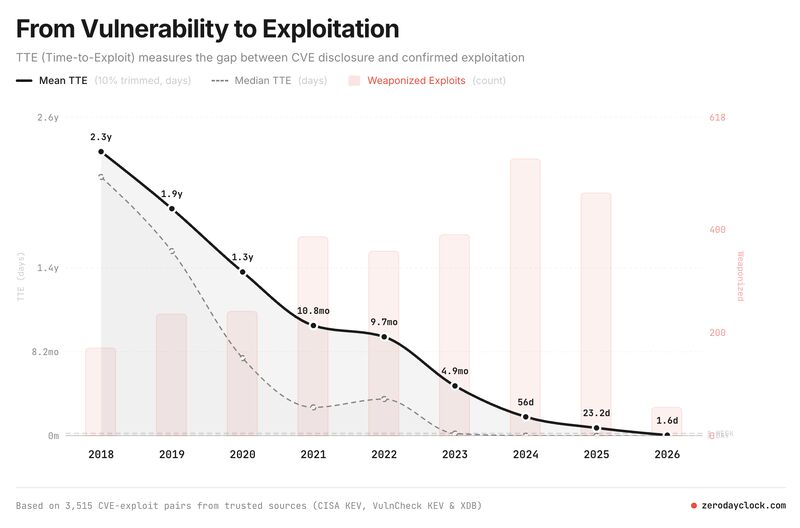
Zero Day Clock: https://zerodayclock.com/ The Zero Day Clock tracks how quickly ...
Partner ecosystem
Integrations and standards support for practical SBOM and AI-BOM workflows.