Blog
Introducing Attestation Signing: Binding SBOMs to Software Artifacts
A signed Software Bill of Materials answers an important question: Has this SBOM changed since an a...
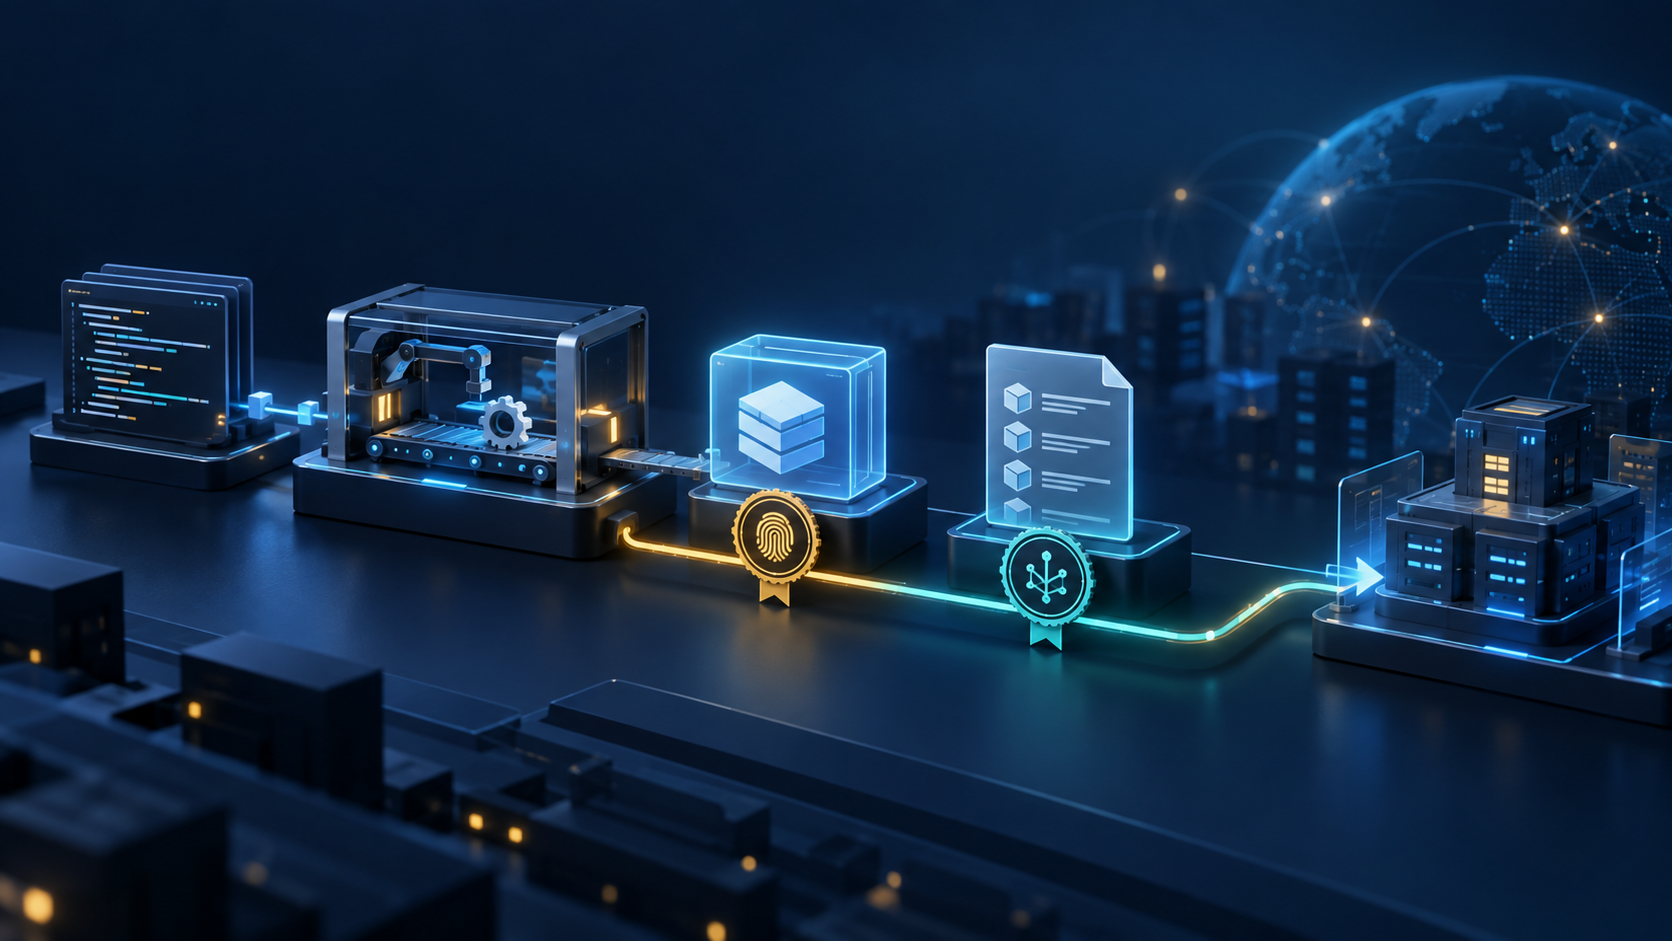
SLSA Secures the Build. Who Secures the SBOM?
Modern software supply chain security is built on evidence. Organizations need confidence in what software contains, whe...
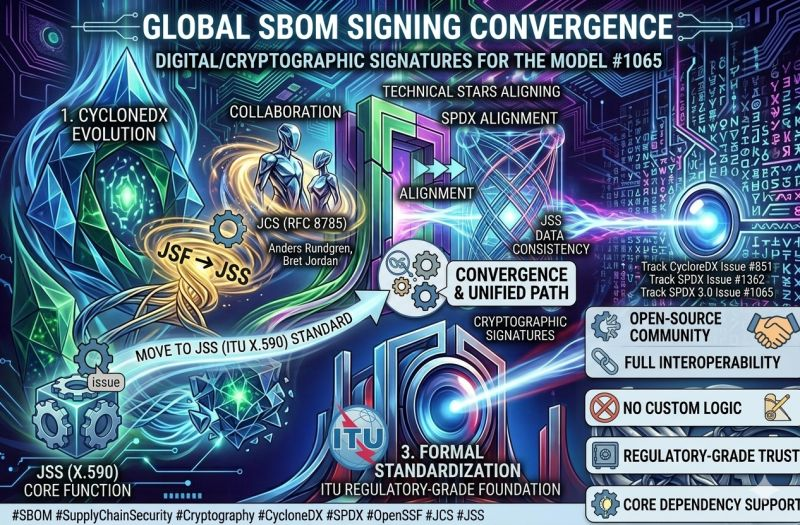
🔀 Convergence in SBOM Signing
“Don’t roll your own crypto.” It’s the first rule of security engineering, and it turns out it’s ...
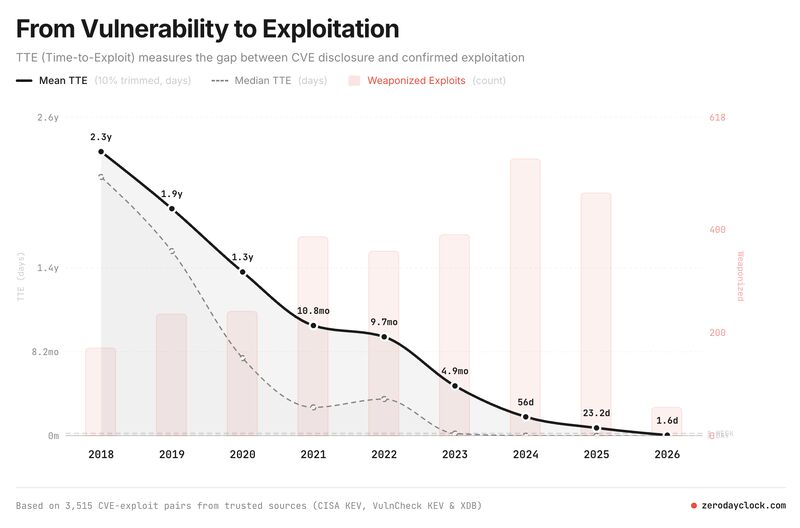
An Interesting and Useful Visualization for Security Teams
Zero Day Clock: https://zerodayclock.com/ The Zero Day Clock tracks how quickly ...
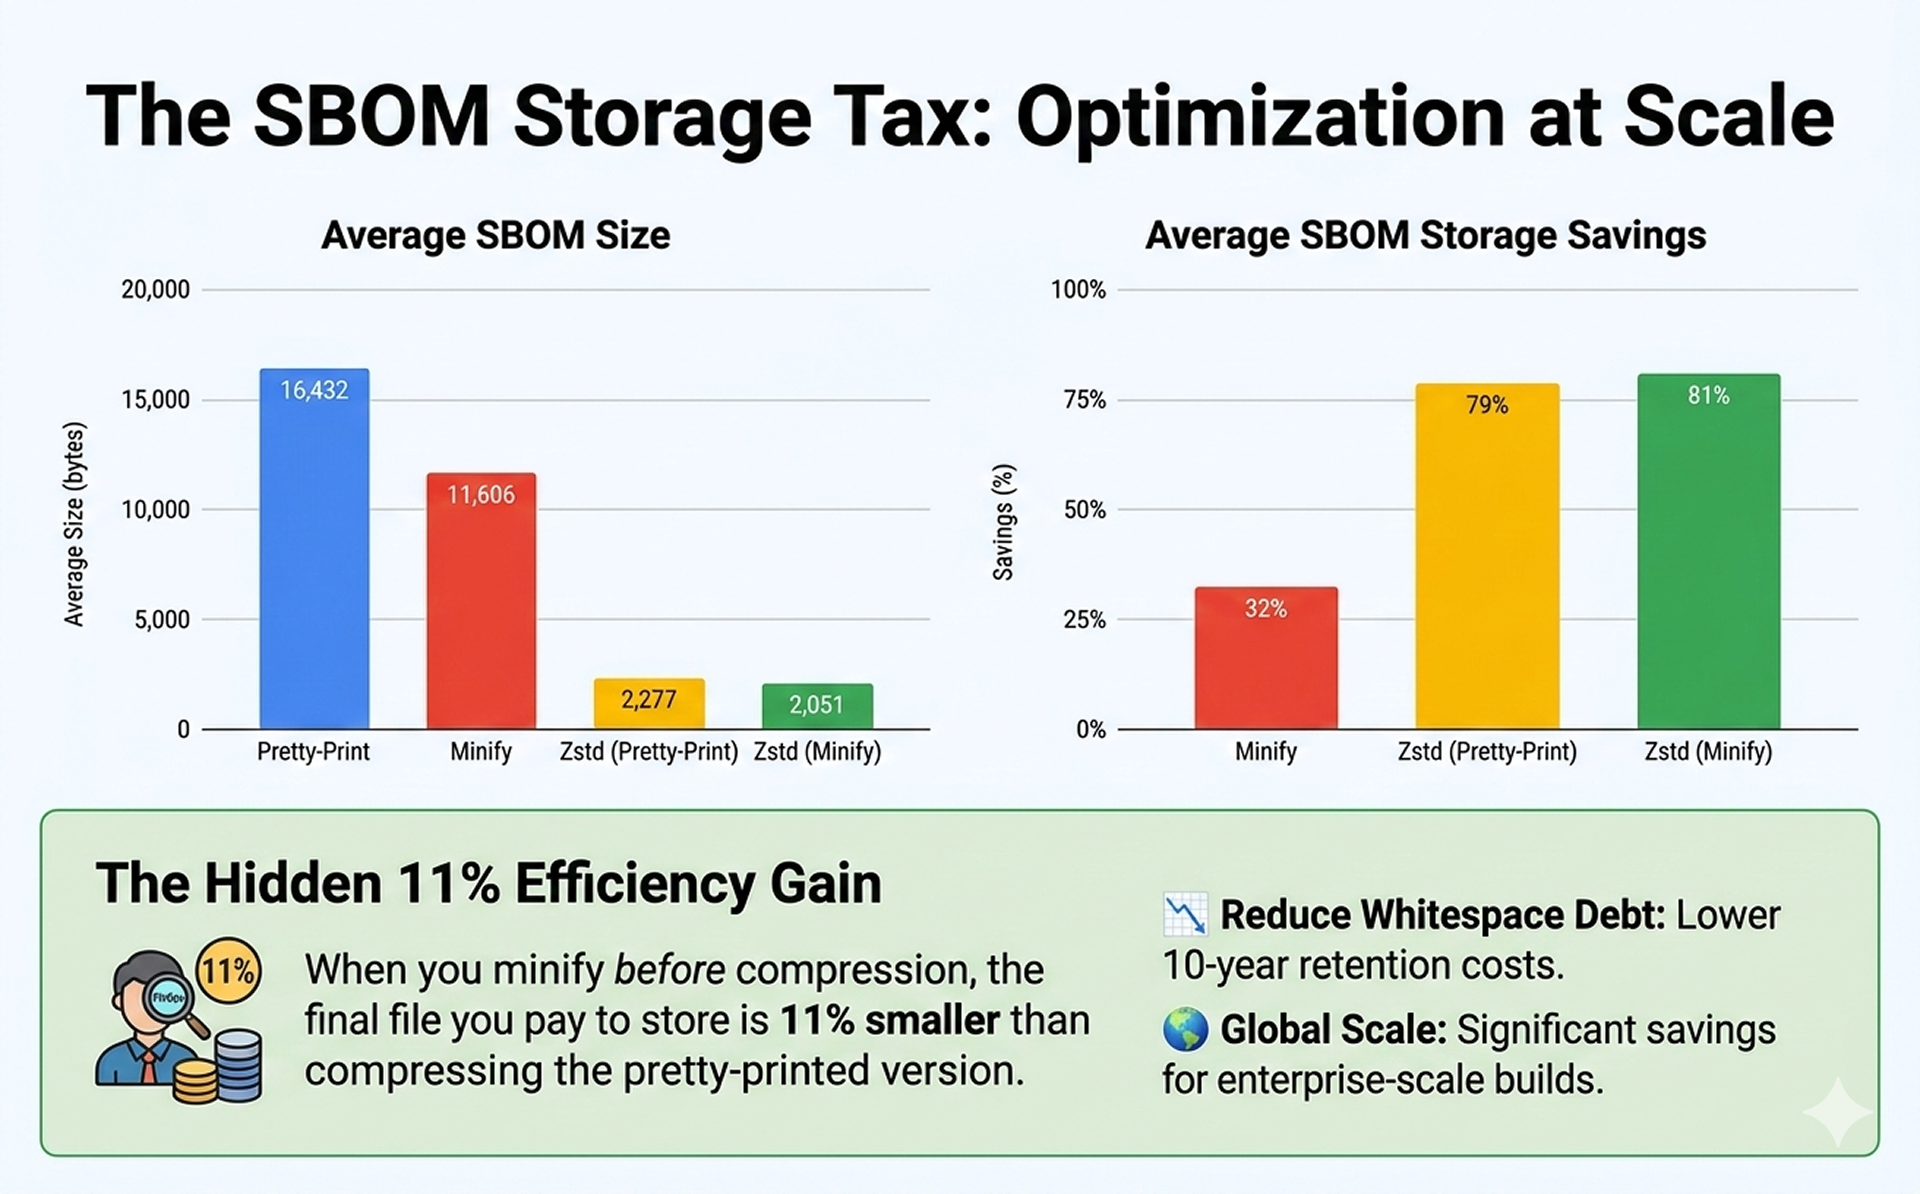
The SBOM Storage Tax: Optimization at Scale
Following my last post on the “Storage Tax” of binary blob signing, I received some insightful feedback from the co...

The SBOM Signature 'Storage Tax': Money Talks 💰📉
Over the last few weeks, I’ve been deep in the weeds of technical best practices for signing SBOMs. I’ve discussed ...