Blog

🚨 Call for Feedback: A Standardized Approach to SBOM Signing
The new benchmark by which all SBOM signing and verification tools will be judged. This Frida...
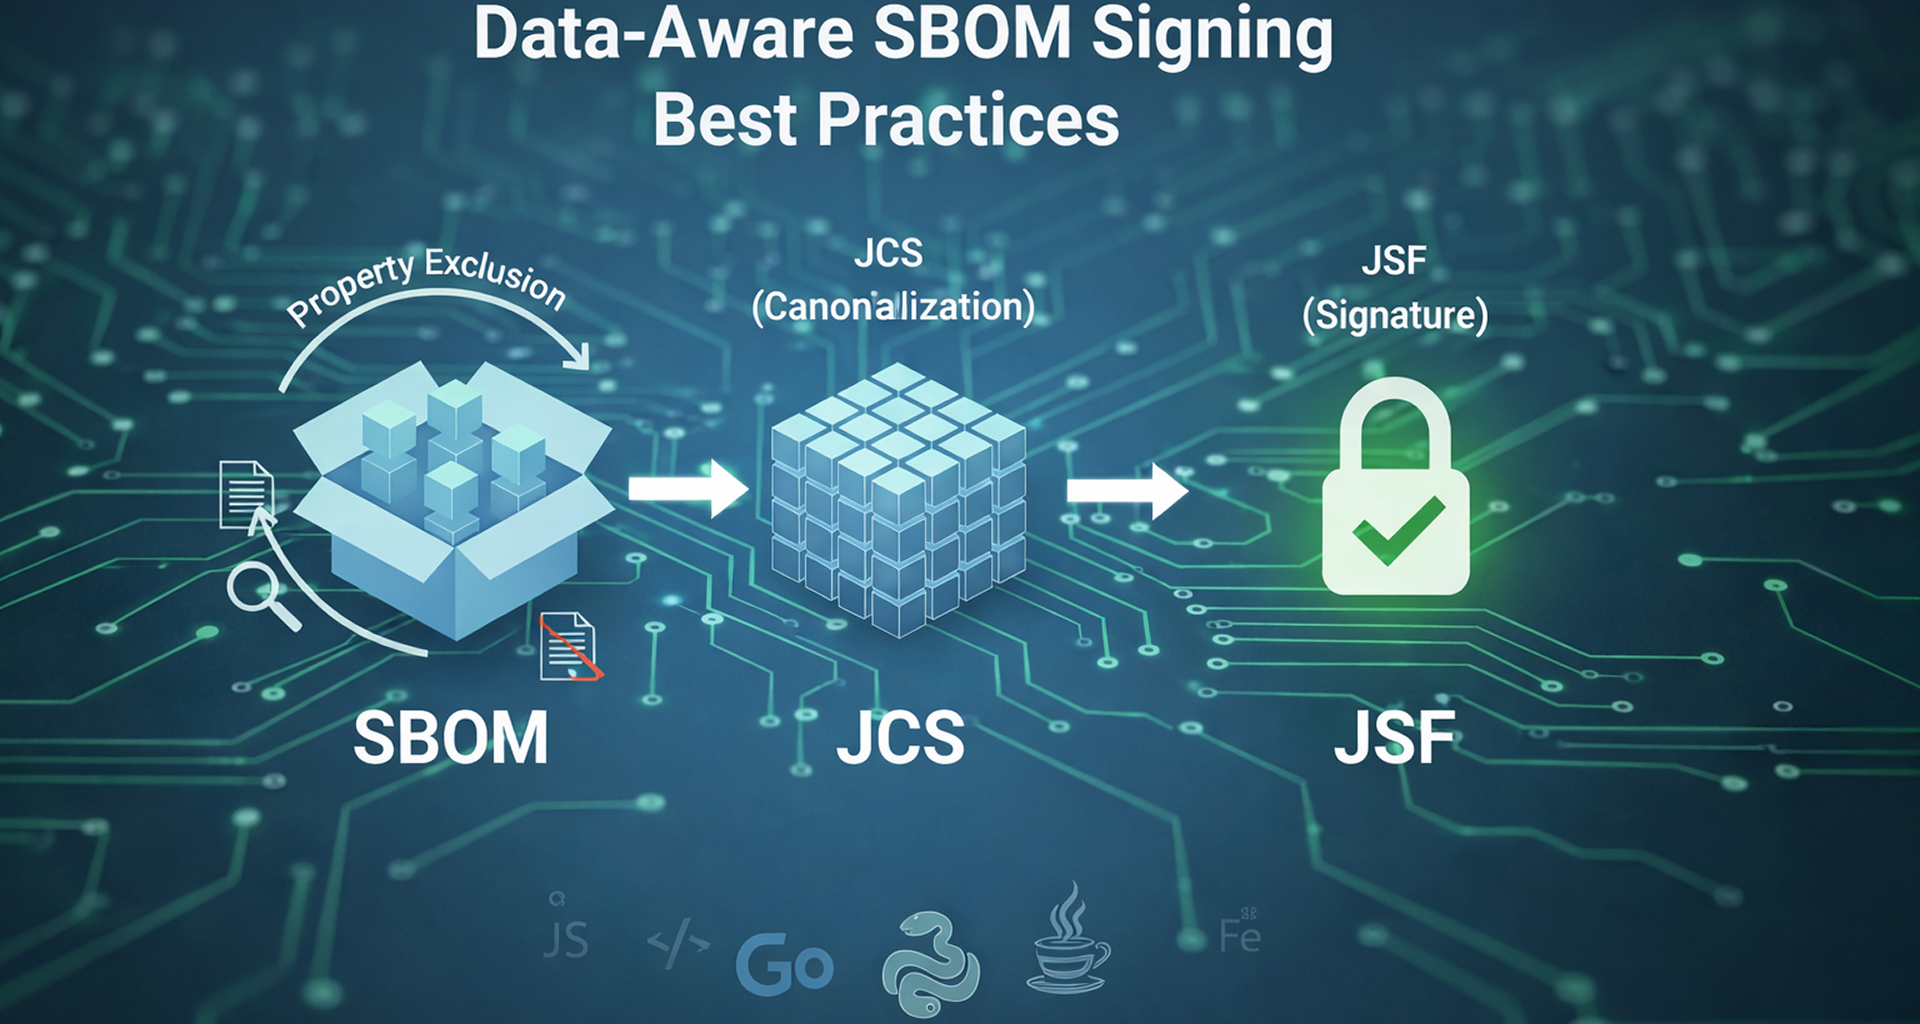
Implementing Data-Aware Signing
I recently argued that with SBOMs we need to stop signing the “container” (the file) and start signing the “c...

Stop Signing the Container 📦, Start Signing the Content
In my current work with the OpenSSF SBOM...

The Binary Blob Trap in SBOM Signing 🪤
Is the industry’s favourite SBOM signing tool actually creating a verific...
Thoughts on ENISA's New SBOM Implementation Guide 🤔
I’ve been diving into the EN...
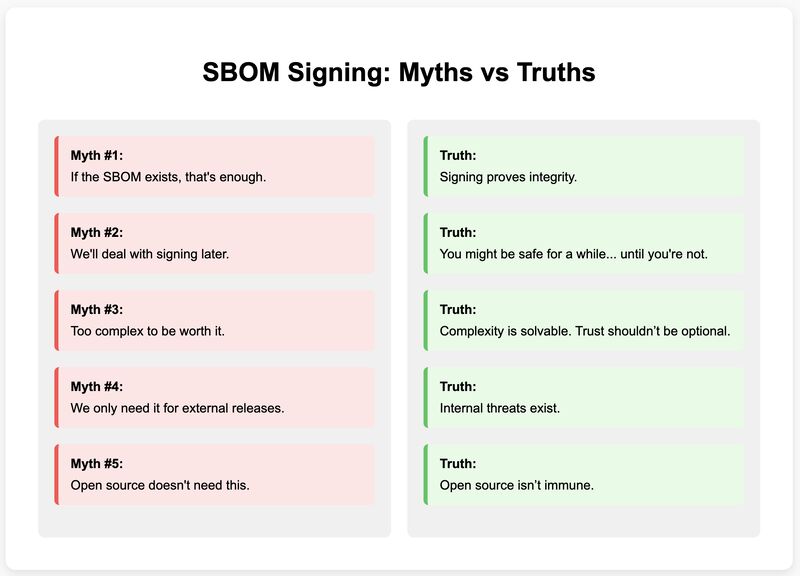
🚨 SBOM Signing: The Myths That Are Putting You at Risk 🔥
“If the SBOM exists, that’s enough” “We’ll deal with signing later” “To...