Blog
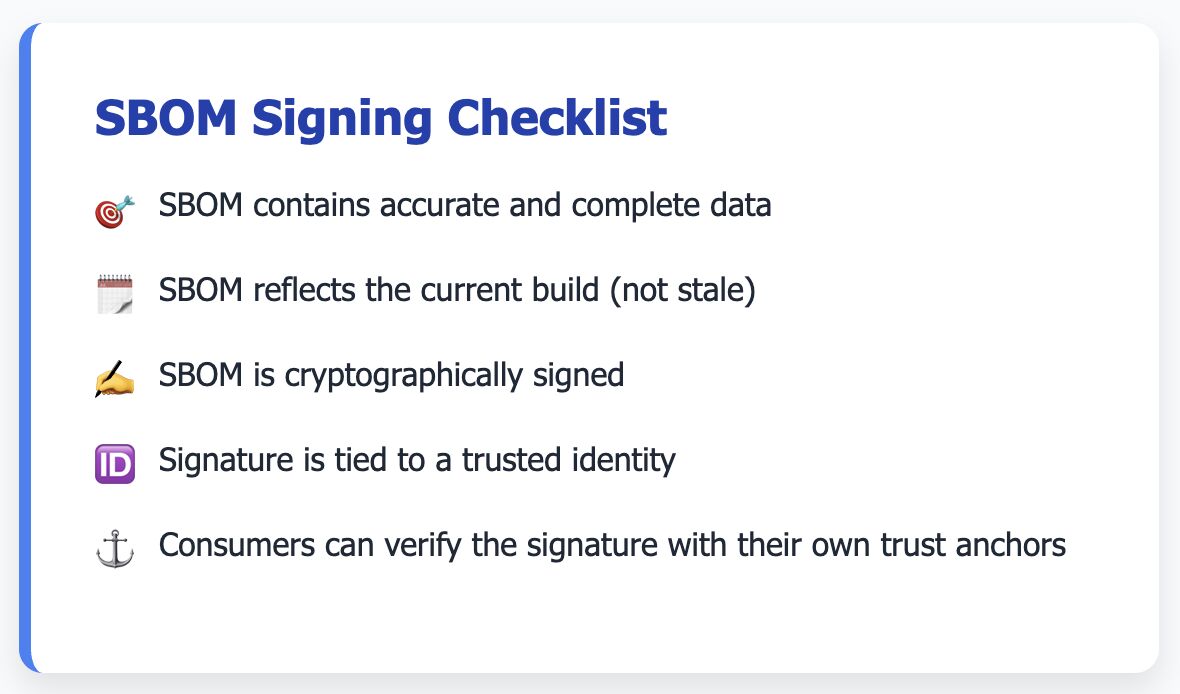
🔏 SBOM Signing ≠ Security
Just because an SBOM is signed doesn’t mean it’s safe. Signing is still important though. It gives you integ...
The Evolution of SBOMs at OwnersBox
I gave a presentation at the CISA SBOM Community Weekly Meeting yesterday where I shared how we approached SBOMs in my latest r...
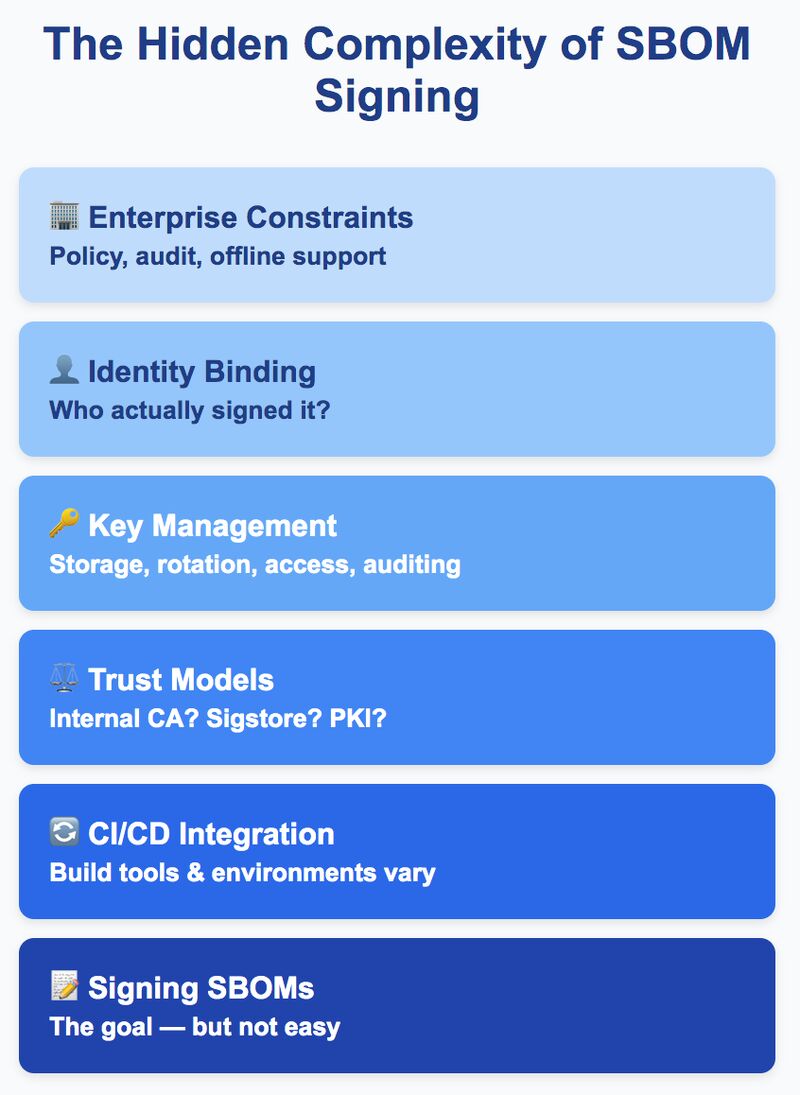
🔐 What Makes Signing SBOMs Hard in Practice?
Everyone agrees SBOMs should be signed. But actually doing it? That’s where things get messy. Let’s t...
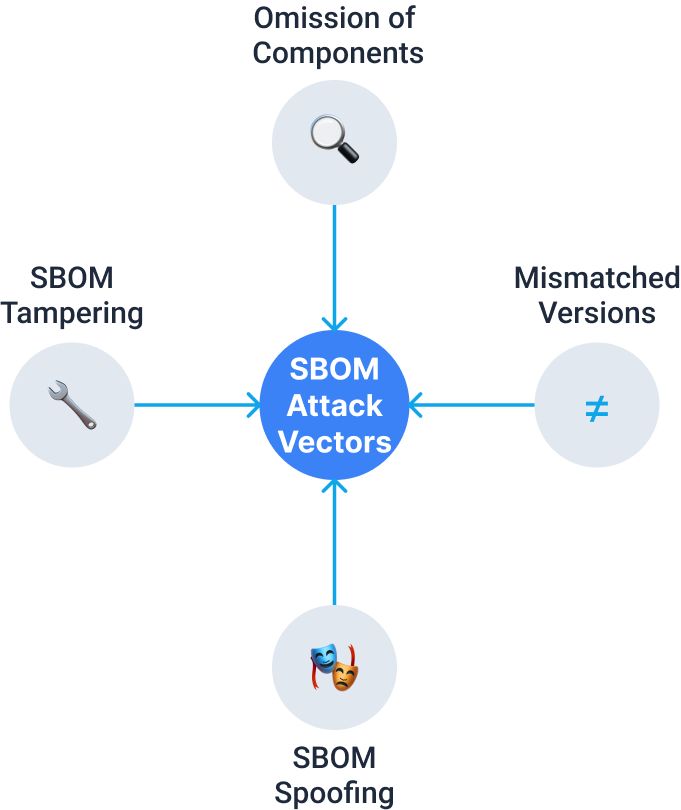
Your SBOM Can Be Hacked 📦💀
Yes, even the one you just generated. An SBOM (Software Bill of Materials) is supposed to bring transparency and trust t...
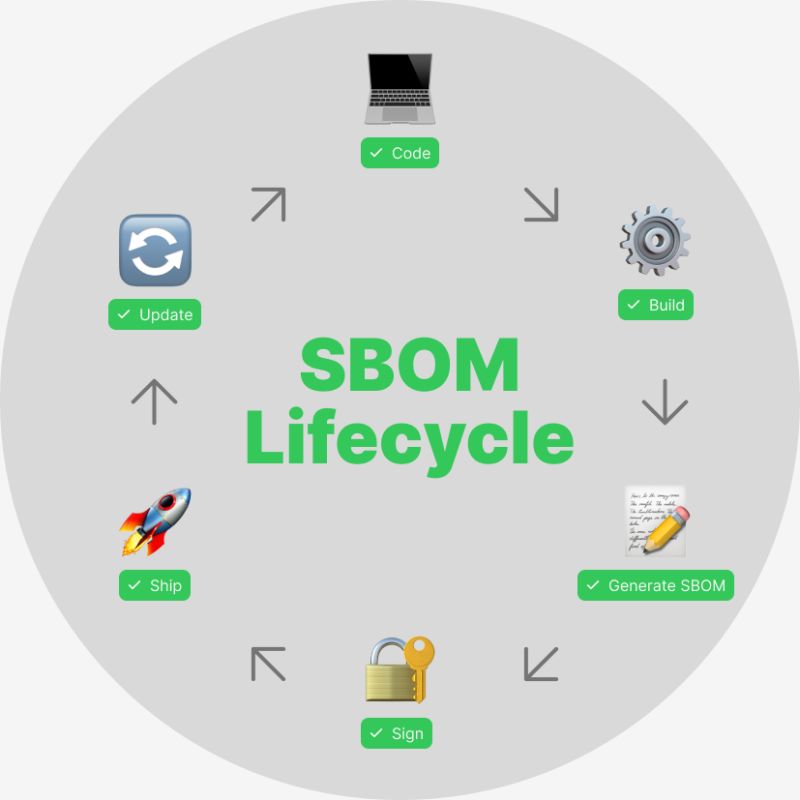
Why SBOMs Are Not One-and-Done 📦🔄
✅ You’ve generated an SBOM. Congratulations! But here’s the truth. An SBOM is not a report you create once a...
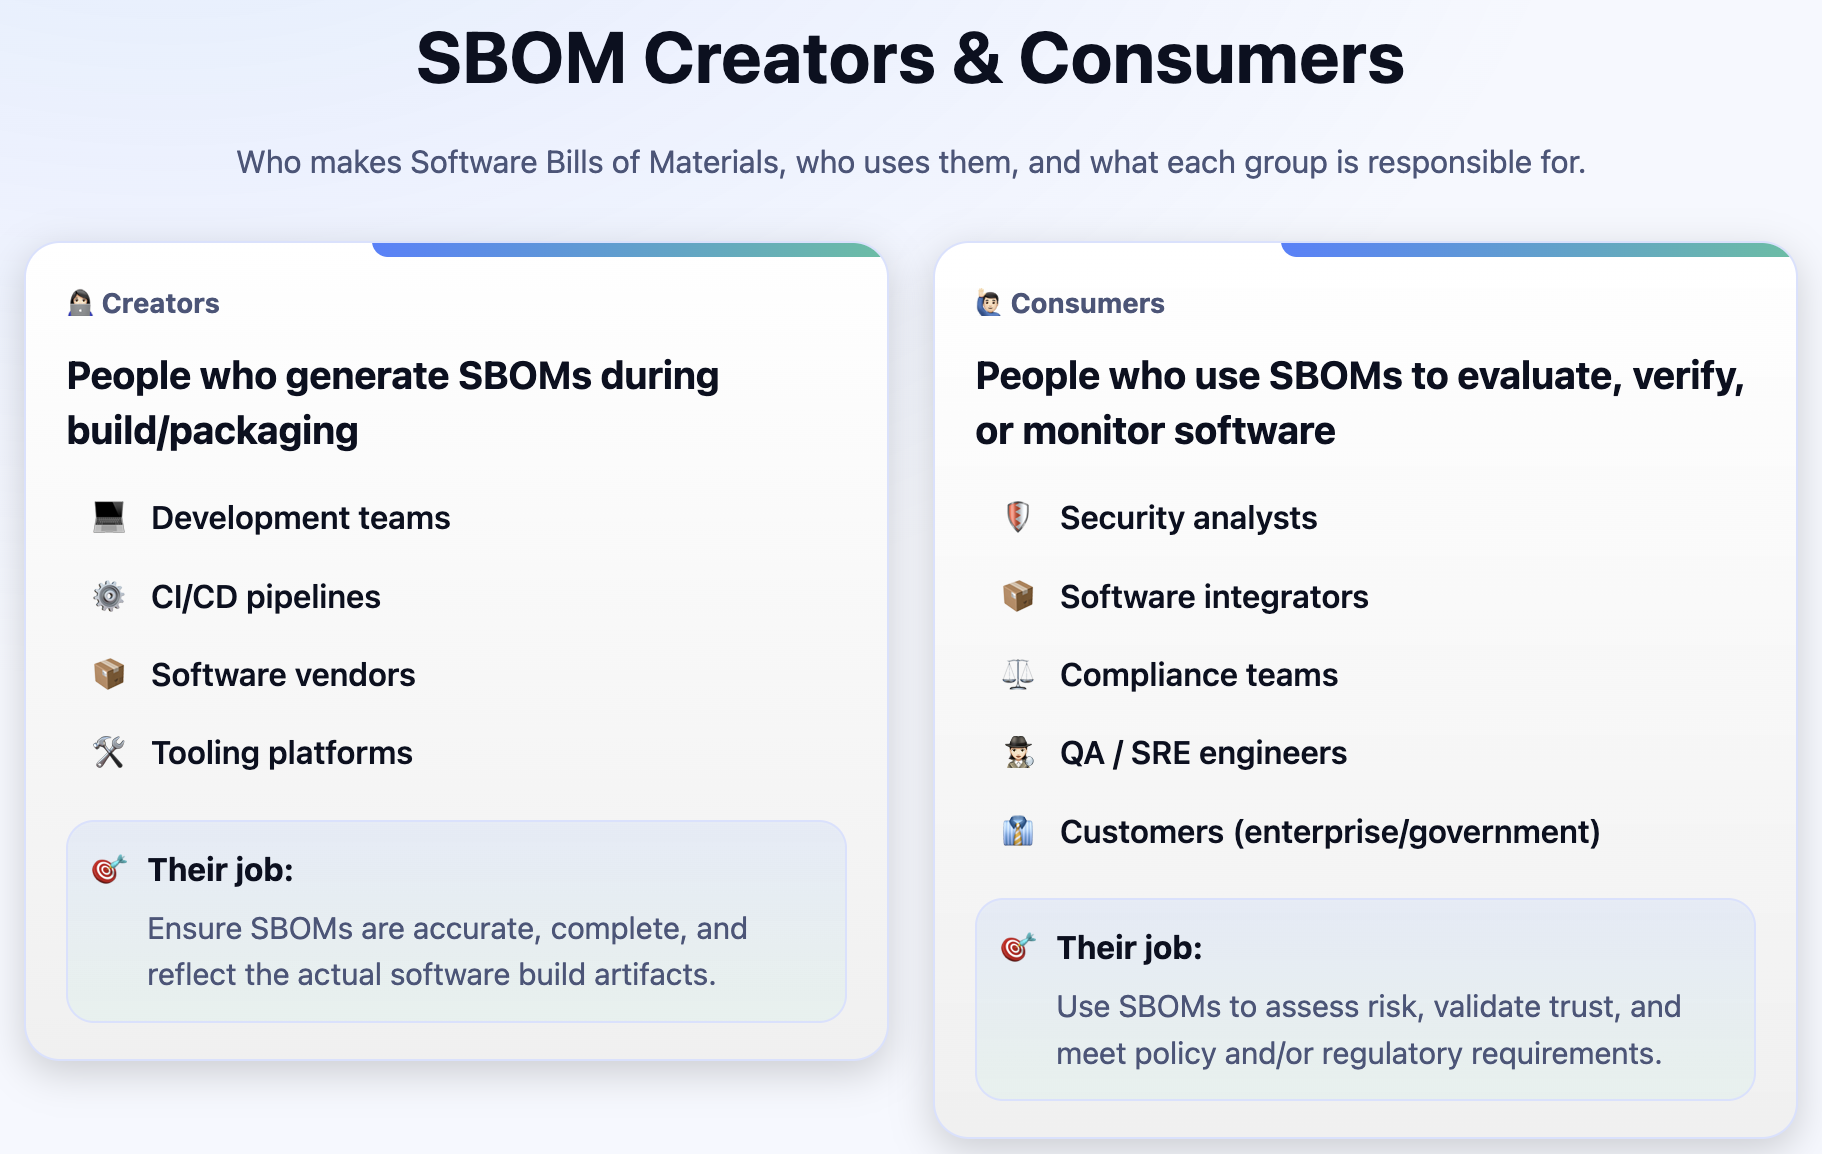
𝗪𝗵𝗼 𝗮𝗰𝘁𝘂𝗮𝗹𝗹𝘆 𝗯𝘂𝗶𝗹𝗱𝘀 𝗦𝗕𝗢𝗠𝘀? 𝗔𝗻𝗱 𝘄𝗵𝗼 𝗻𝗲𝗲𝗱𝘀 𝘁𝗵𝗲𝗺? 🤔🔍
SBOMs are a critical tool for understanding your software supply chain. But not everyone touches an SBOM the same way. T...